


AML and KYC Software Development: How Banks and Fintechs Build Compliance They Own
 Andrew BurakCEO and Founder at Relevant Software
Financial institutions spend $206.1 billion a year on financial crime compliance, and nearly all of them say the bill keeps growing. Labor is the biggest line in that budget, with people reviewing alerts and chasing documents by hand. At the same time, 67% of banks have lost clients because onboarding and KYC took too long. So compliance costs you twice, once in salaries and again in customers who walk away.
The pressure won’t ease in 2027. The EU’s new AML Regulation (AMLR) applies from 10 July 2027, and the new EU authority AMLA starts supervising the riskiest institutions directly in 2028. Any system that can’t show regulators how it reached a decision becomes a liability. In this article, Relevant Software looks at AML and KYC software development from a business angle. We’ll cover the modules you need, when to build, buy, or combine both, what weak systems cost, and how we design AML and KYC development solutions for banks and fintechs.
Key takeaways
- Compliance spending keeps climbing. In the US and Canada alone it reached $61 billion a year, and 99% of institutions report higher costs.
- Slow KYC loses revenue. Two-thirds of banks lost clients to slow onboarding, and only 4% have automated most of their KYC workflows.
- Fines move with the regulators. AML, KYC, sanctions, and CDD penalties reached $3.8 billion in 2025. US totals fell, while EMEA penalties grew 767%.
- Rule-based monitoring wastes analyst time. Studies of legacy systems report false positive rates of 95 to 98%, while machine learning triage cut false positives by 80% and still caught over 90% of true positives.
- The AML software market is set to grow from $4.13 billion in 2025 to $9.38 billion by 2030, with KYC, CDD, and sanctions screening holding the largest share.
- A hybrid approach often wins. You buy commodity checks such as ID verification through APIs and own the logic that makes your risk decisions.
KYC vs AML: how they work together across the customer lifecycle
KYC and AML often get lumped together, but they answer different questions at different moments. KYC asks “Who is this customer, and how risky are they?” when the relationship starts. AML asks “Is anything this customer does now suspicious?” for as long as the relationship lasts.
KYC (Know Your Customer) is the process of verifying a customer’s identity. During onboarding, it collects:
- identity data: name, date of birth, address, nationality;
- the source of funds;
- links to illicit activity, found through background checks;
- political exposure, meaning whether the person is a politically exposed person (PEP) or close to one.
AML (anti-money laundering) is the wider set of obligations a regulated business must meet. KYC sits inside it, along with record-keeping for the period your regulator sets, ongoing monitoring, sanctions screening, and reporting suspicious activity to your financial intelligence unit (FinCEN in the US, for example).
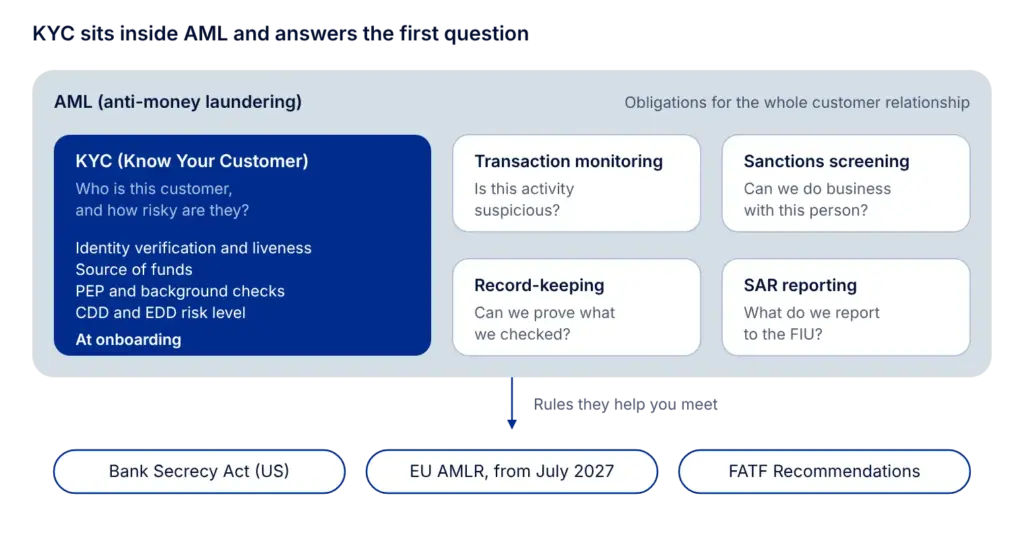
KYC answers the onboarding question; the rest of the AML stack keeps asking its own questions for as long as the customer stays.
KYC is the foundation. You can only manage the risk of a customer you’ve identified correctly. When the two run as separate tools, you pay for it: the same customer gets checked twice, a risk score from onboarding never reaches the monitoring engine, and an investigator rebuilds the customer’s story from five screens.
A connected AML and KYC stack follows the customer through four stages:
- Onboarding. Identity verification, document checks, and sanctions and PEP screening decide whether you can open the account.
- Risk assessment. Customer due diligence (CDD) assigns a risk level. High-risk customers get enhanced due diligence (EDD), including source of wealth.
- Ongoing monitoring. Transaction monitoring and periodic rescreening catch changes in behavior or status.
- Investigation and reporting. Alerts become cases, cases become decisions, and confirmed suspicions become suspicious activity reports (SARs).
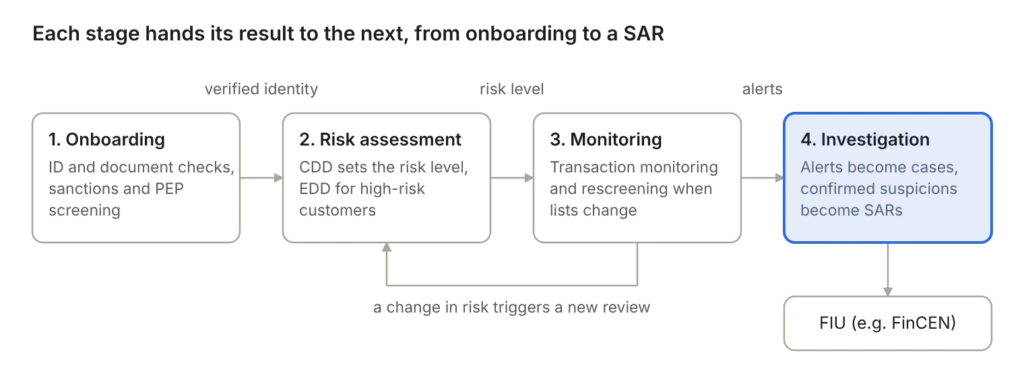
Each stage needs its own module. Let’s look at what those modules do and which features matter.
AML and KYC software modules and features that cut compliance workload
The modules that cut compliance workload the most are identity verification, CDD and EDD risk scoring, KYB, sanctions and PEP screening, transaction monitoring, case management with SAR reporting, and perpetual KYC. Together they cover a customer from the first ID check to the last suspicious activity report. The table sums up the must-have features of each, and the sections below explain what each module saves your team.
AML and KYC modules at a glance
| Module | Must-have features | Business result |
|---|---|---|
| Identity verification | Document OCR, liveness, device signals | Fewer abandoned applications, fewer fake accounts |
| CDD and EDD | Configurable risk model, explainable scores | Analyst time goes to high-risk clients |
| KYB | Registry lookups, ownership graphs | Safe onboarding of merchants and partners |
| Screening | Fuzzy matching, automatic rescreening | Fewer manual list checks |
| Transaction monitoring | Rules plus ML scoring, full rail coverage | Fewer false positives, no blind spots |
| Case management and SAR | Evidence packs, SAR drafting, four-eyes approval | Faster investigations that pass audits |
| Perpetual KYC | Event triggers, audit trail | Lower review costs, current customer data |
Identity verification and liveness checks that reduce onboarding drop-off
This is where you win or lose a new customer. Signicat’s research found that 68% of European consumers abandoned a financial application during onboarding in 2022, up from 40% in 2016. Every extra form field and manual review step adds to that number.
Fraudsters work this stage too. FinCEN has seen a rise in suspicious activity reports describing deepfake media used to get past identity checks since 2023. Its red flags include photos that don’t match the stated age, third-party webcam plugins during live checks, and customers who decline multifactor authentication.
What to build in from day one:
- scan-based document capture with OCR and automated authenticity checks;
- biometric face match and liveness detection that resists injected video;
- device, IP, and geolocation signals compared against the documents;
- a fallback path to manual review that doesn’t lose the applicant.
Customer risk scoring (CDD and EDD) that focuses analysts on high-risk clients
Customer due diligence turns raw onboarding data into a risk level. That level decides how much scrutiny each customer gets later. The EU’s AMLR makes this risk-based approach mandatory: simplified due diligence for low-risk cases, and enhanced due diligence covering source of funds, source of wealth, and PEP exposure for high-risk ones. Former PEPs stay under enhanced due diligence for at least 12 months after they leave office.
Your CDD engine should give you:
- a configurable risk model your compliance team can change without a code release;
- automatic routing to simplified, standard, or enhanced due diligence;
- a record of which factors drove each score, so you can explain it in an audit.
KYB verification for business clients, merchants, and partners
KYB (Know Your Business) is KYC for companies. The hard part is finding the people behind the company. Under the AMLR, ownership of 25% or more of shares or voting rights makes someone a beneficial owner, and both direct and indirect holdings count.
Look for company registry lookups, ownership graph building, beneficial owner screening, and document collection for directors.
KYB matters most for marketplaces, payment facilitators, and platforms that pay out to sellers. In those businesses, seller checks can’t live apart from payments. When a platform moves to custom payment processing software, KYC and KYB checks for sellers and partners sit in the same flow as payouts and pre-authorization risk scoring.
Sanctions, PEP, and adverse media screening without manual list checks
Every new customer, counterparty, and payment gets checked against sanctions lists, PEP databases, and negative news. In theory, that’s a simple lookup. In practice, it’s one of the noisiest jobs in compliance: LexisNexis found that screening alerts rose at 83% of mid and large institutions in the US and Canada.
And the data you screen keeps growing. Once FATF’s revised Recommendation 16 takes effect, cross-border payments above USD/EUR 1,000 must carry the sender’s and recipient’s name, address, and date of birth by the end of 2030.
A screening module worth paying for needs fuzzy name matching with transliteration, automatic list updates, rescreening of existing customers whenever a list changes, and match explanations your analysts can trust.
Transaction monitoring that flags real risk, with fewer false positives
Gaps in this module draw some of the heaviest penalties. TD Bank’s 2024 guilty plea shows why: 92% of its transaction volume went unmonitored between 2018 and 2024, about $18.3 trillion in activity, and its monitoring program stayed effectively static for years. The bank agreed to pay over $1.88 billion to the Justice Department alone.
The opposite problem is just as expensive. Rule-based systems report false positive rates of around 95 to 98%, so analysts spend most of their day closing alerts that mean nothing.
The way out is detection logic built around your actual transaction patterns. It should cover typologies such as structuring, layering, smurfing, mule accounts, and synthetic identities across wires, ACH, SEPA, and card rails, with rules your team can tune and defend to a regulator.
Four features keep monitoring defensible:
- real-time and batch monitoring across every payment rail you support;
- a rules engine your analysts can configure and backtest;
- machine learning scoring that ranks alerts by risk;
- coverage reporting, so you can prove no transaction type slips through.
Case management and SAR reporting that hold up in an audit
An alert is only useful if someone can act on it fast. Case management gives investigators one view of the customer, the alert, and the evidence. Many teams model this with a business process management (BPM) engine and BPMN 2.0 workflows, using decision tables to load risk indicators and route cases.
At minimum, investigators need alert grouping by customer, escalation rules, four-eyes approval, SAR and CTR drafting, and filing to your financial intelligence unit.
Much of this work is repetitive evidence gathering, which makes it a good fit for AI. Agents can attach the evidence to each alert, assemble KYC and KYB verification packs from source documents, and prepare first-draft SARs and CTRs for a compliance officer to review and file.
Perpetual KYC that keeps customer profiles current between reviews
Periodic KYC reviews are costly. Fenergo estimates that annual KYC reviews cost $60 million for a corporate and institutional bank and $175 million for a commercial bank. Perpetual KYC (pKYC) replaces calendar-based reviews with event-driven ones. A change in ownership, a new sanctions hit, or unusual activity triggers a review of that customer only.
To make it work, you need event triggers from monitoring and screening, automatic data refresh from registries, and a full audit trail of every change to the customer record.
Build, buy, or hybrid: choosing the AML and KYC approach that won’t lock you in
Knowing the modules is half the decision. The other half is whether you build them, buy them, or mix the two. There’s no single right answer here. The right choice depends on how much of your risk logic is unique and how fast your volumes grow.
Buy an off-the-shelf platform when you need to launch fast, your risk profile is standard, and volumes are small. You can go live quickly. The trade-off shows up later: per-check or per-seat fees grow with your customer base, and the detection rules belong to the vendor.
Build a custom system when monitoring logic is part of your competitive edge, you operate across several jurisdictions, or license fees have started eating your margin. You own the code, the rules, and the data. The trade-off is a bigger upfront investment and the need for a team that understands both engineering and compliance.
Go hybrid when you want both. You buy commodity checks such as document verification, sanctions data, and bank connections through KYC and AML API integration, and you build the orchestration layer, risk logic, and case management that make your decisions.
| Buy | Build | Hybrid | |
|---|---|---|---|
| Time to launch | Fastest | Slowest | Fast for the first release |
| Cost over time | Grows with volume | Mostly upfront, then maintenance | Vendor fees only for commodity checks |
| Control over rules | Vendor’s | Yours | Yours for decisions, vendor’s for data |
| Vendor lock-in | High | None | Limited to replaceable APIs |
| Best for | Early-stage, single market | Banks, multi-jurisdiction players | Growing fintechs |
Two of our projects show how this plays out.
For Fisk, a US fintech MVP for automated investing and virtual card tipping, we went hybrid. KYC, card issuing, payment processing, and bank account connections ran through Plaid, Galileo, and Stripe. Our team built the product around them, including the integrations with all three financial APIs and bank linking across 11,000+ institutions through Plaid. The client got working KYC without building identity verification from scratch, and the MVP shipped within the agreed budget and timeline.
A licensed Caribbean lender took the build route for the opposite reason. Its vendor platform charged high license fees and couldn’t adapt. We replaced it with a custom loan management platform. The lender now saves $100,000 a year on licensing, cut processing time from 30 seconds to 3 seconds, and handles twice the loan volume with the same team.
What outdated AML and KYC systems cost your business
Whichever path you pick, the cost of standing still is easy to underestimate. Here’s what outdated AML and KYC systems cost in practice.
| Challenge | What it costs you | Service that fixes the issue |
|---|---|---|
| Regulatory fines | $3.8B in AML, KYC, sanctions, and CDD penalties in 2025; EMEA penalties up 767% | Transaction monitoring software development |
| False positives | 95 to 98% of rule-based alerts can be false; screening alerts rose at 83% of mid and large institutions | AI transaction monitoring, AI agents for compliance |
| Slow onboarding | 67% of banks lost clients to slow KYC; only 4% automated most KYC workflows | Digital onboarding and KYC within digital bank platform development |
| Expensive legacy vendors | 79% of institutions saw higher compliance and KYC software costs | Monitoring system modernization, banking software development |
| Regulatory change | AMLR applies from July 2027; FATF payment data rules by end of 2030 | Configurable rules engine, AI compliance services |
| Deepfakes and synthetic IDs | Rising deepfake SARs since 2023; fraud losses plus reporting failures | Identity verification with liveness and device signals |
| AI you can’t explain | Models a supervisor can’t audit block approval or trigger findings | AI agent governance platform development |
Regulatory fines and enforcement actions
Penalties shift with the regulators, and right now they’re moving toward Europe and Asia. Fenergo counted $3.8 billion in AML, KYC, sanctions, and CDD penalties in 2025. North American totals fell 58%, while EMEA penalties rose 767% and APAC penalties rose 44%. Almost a quarter of the top ten fines involved digital asset firms. Transaction monitoring failures were among the drivers, including a $59 million FCA fine on a UK building society.
For your business, that means a quiet year in one market says little about the next one. If you operate in the EU or plan to, AMLA gets the power to impose financial sanctions for serious, systematic, or repeated breaches.
Monitoring failures sit behind many of these cases, so that’s where the fix starts. Custom transaction monitoring software gives you detection logic built around your own transaction patterns, coverage across every rail you support (wires, ACH, SEPA, and cards), and rules your analysts can backtest and defend in front of a regulator. Before it goes live, it runs in shadow mode on real traffic, so you see the gaps it closes before you depend on it.
False positives that bury your analysts
Rule-based monitoring flags anything that crosses a threshold. The result is a queue where 95 to 98% of alerts can be false positives. Every one of them still needs a person to open, review, and close it. That’s why labor ranks as the largest compliance cost, and why 83% of mid and large institutions in the US and Canada saw screening alerts grow.
Hiring more analysts doesn’t scale. Better scoring does. In the same study by Feedzai and the University of Porto, a machine learning triage model cut false positives by 80% compared to the rule system and still detected over 90% of true positives. For a compliance team, that’s most of the queue gone, with the real cases still caught.
Better scoring shrinks the queue. AI shortens the work on what’s left. AI agents built for compliance and audit automation attach the evidence to each alert, assemble KYC and KYB verification packs from source documents, and draft SARs and CTRs. Your analysts spend their time on review and decisions, and a compliance officer still signs off on every filing.
Slow onboarding that sends customers to competitors
Two-thirds of banks have lost clients because onboarding and KYC took too long, and the share grew 19% in a year. Only 4% of banks have automated most of their KYC workflows. Every manual step is a point where a customer opens a competitor’s app instead.
Now put a price on it. Fenergo estimates that a single medium-risk KYC review costs $2,250 at a corporate bank and $2,089 at a commercial one. Across books of 26,800 and 83,800 such clients, that’s $60 million and $175 million a year. And that’s only the cost of reviewing customers you keep. Every applicant who quits halfway also takes the marketing and sales spend that brought them in.
The checks themselves aren’t what banks blame. In the same Fenergo study, banks that lost clients named three causes:
- poor data management and siloed processes (86%);
- poor customer experience and process delays (77%);
- complex onboarding processes (45%).
All three are software problems, which means they can be fixed. A single customer data layer stops teams from asking for the same documents twice. Straight-through processing approves low-risk applicants without waiting for a person. Reviewers only open the cases that need judgment. For Swift Onboard, a custom registration flow brought contractor setup down to under 10 minutes.
The same approach scales to a whole bank. In digital bank platform development projects, identity verification is one part of a wider onboarding flow that opens an account in minutes. Here’s how we build it and fit it to where the bank starts:
- The flow itself. Remote identity verification, document checks, and risk scoring run as one journey. FinCEN’s recommended controls (phishing-resistant MFA, live verification, and deepfake detection) are built into it as steps, so the applicant meets them in one pass.
- Your choice of KYC vendor. The flow connects to the KYC and AML providers you pick through their APIs. If a vendor’s pricing or accuracy stops working for you, you swap it and keep the journey, the risk rules, and the data.
- Three starting points. We add a digital onboarding layer on top of the core you already run, migrate the core in waves with parallel runs, or launch on BaaS and move to your own core later. You don’t have to replace a core to get faster onboarding.
- AI with human sign-off. AI agents handle routine document checks and onboarding reviews. A person approves wherever regulation requires it, and every decision lands in a full audit trail.
- Compliance before code. Data flows and controls are agreed with your compliance team before development starts, covering GDPR, PSD2, DORA, and data residency rules. Our processes are ISO 27001:2022 certified.
Legacy vendors that charge more every year
Among US and Canadian institutions, 79% saw higher costs for compliance and KYC software. Rigid platforms also slow you down when the rules change, because every adjustment waits for the vendor’s roadmap. Our Caribbean lender client cut $100,000 a year in license fees by replacing such a platform.
License fees are only the visible part of the bill. The same lender also cut maintenance costs by 4x after the switch and now processes twice as many loans with the same team. That’s the money a rigid platform was quietly absorbing.
Leaving a vendor doesn’t have to mean a risky big-bang launch. Monitoring system modernization runs the old and new systems in parallel, reconciles their results transaction by transaction, and keeps a rollback plan for each wave, so monitoring coverage never drops during the move. And since the AML and KYC layer sits right next to core banking, lending, and payments, it often makes sense to modernize them together. Banking software development covers core banking, lending, payments, and RegTech tools, so new compliance modules plug into the systems around them from day one.
Regulatory change you can’t keep up with
The rulebook is moving on several fronts at once. The EU AMLR applies from 10 July 2027 and brings crypto firms, luxury goods traders, and football clubs into scope, along with a €10,000 cap on cash payments. In crypto, 83% of surveyed jurisdictions have passed Travel Rule legislation, and FATF reports that most identified on-chain illicit activity now involves stablecoins.
A system with hardcoded rules turns each of these changes into a development project. A configurable rules engine turns them into a settings change your compliance team can make and test.
Deepfakes and synthetic identities at onboarding
Generative AI makes fake documents and faces cheap. FinCEN has warned that criminals use deepfake media to get past identity verification and authentication, and it recommends phishing-resistant multifactor authentication, live verification checks, and deepfake detection tools. A fake account that slips through onboarding becomes a mule account in your transaction monitoring queue later.
The bill is growing fast. Deloitte projects that generative AI could push US fraud losses to $40 billion by 2027, up from $12.3 billion in 2023, a 32% annual growth rate. Synthetic identities alone cost an estimated $20 billion in 2020, according to the Federal Reserve Bank of Boston.
For a lender or fintech, that loss arrives in three forms:
- Credit write-offs. A synthetic identity applies again and again until it’s approved, builds a clean history, earns higher limits, and then disappears with the money. There’s no real person to collect from.
- Reporting failures. FinCEN’s alert reminds institutions of their Bank Secrecy Act reporting duties in deepfake cases. A fake account you didn’t catch can turn into a SAR you didn’t file.
- Operational drag. Every fake account that gets in later produces alerts, investigations, and case work for your monitoring team.
That’s why the front door matters most. At onboarding, stopping a fake identity takes a liveness check and a device-to-document comparison. Once it’s inside, the same identity costs you an investigation, possibly a SAR, and often a write-off.
AI that regulators can’t audit
Machine learning reduces false positives, but only if your risk and compliance teams can approve it. Model risk management rules expect you to show why a model flagged or cleared a customer. AI agents that triage AML alerts need the same scrutiny, which is why a governance platform for AI agents in financial operations wraps them in a policy and permission layer, tamper-evident logs, segregation of duties, and maker-checker rules.
8 use cases where AML and KYC software pays off
The same modules show up in every regulated business, but the priority changes with the product. Here’s where AML and KYC software development pays off first, including projects we’ve delivered.
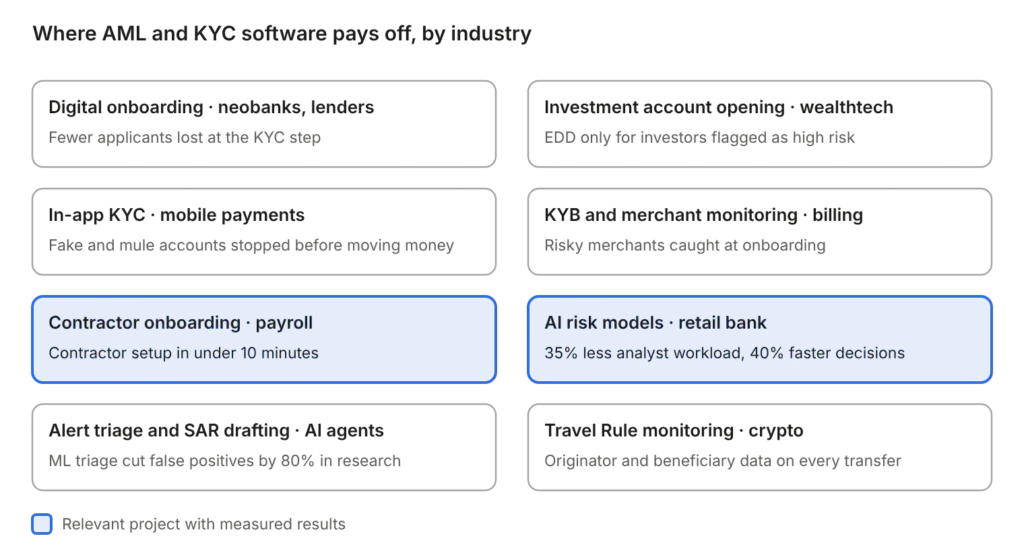
Digital onboarding for neobanks and digital lenders
A customer downloads the app, scans an ID, takes a selfie, and gets an account. Behind that flow sit document checks, liveness detection, sanctions and PEP screening, and a CDD risk score that decides whether the case goes straight through or to a reviewer.
Impact: fewer applicants lost at the step where two-thirds of banks already lose clients, and reviewers who see only the cases that need a human.
Investment account opening in wealthtech
Investment platforms need to know where the money comes from before they accept it. In custom wealthtech software such as robo-advisors, portfolio tools, and micro-investment apps, KYC belongs in the account opening flow, and source-of-wealth checks are triggered only for investors the risk model marks as high risk.
Impact: standard investors fund their accounts without waiting for a manual review, while enhanced due diligence stays focused where the AMLR requires it.
In-app KYC and fraud signals for mobile payments
Mobile payment apps see the device, the IP address, and the session, which is exactly the data FinCEN lists in its deepfake red flags. In mobile payment software, those signals work in two places: at onboarding, to catch mismatches with the ID, and after it, to spot rapid transactions from new accounts and coordinated activity across similar ones.
Impact: fake and mule accounts get stopped before they move money, which protects both your fraud losses and your reporting record.
KYB and merchant monitoring for billing and subscription businesses
Platforms that bill on behalf of merchants carry their merchants’ risk. KYB checks the business and its owners at onboarding. Transaction monitoring then watches for typologies such as card testing and transaction laundering. Both work best when they plug into the billing software that already holds merchant and payment data.
Impact: risky merchants get caught at the door or early in the relationship, before chargebacks and regulatory questions pile up.
Contractor and client onboarding in payroll
Payroll and accounting firms onboard people and businesses at scale, collecting documents and contracts along the way. For Swift Onboard, a UK fintech, we built a registration app where contractors upload and sign documents and staff track every application by stage.
Impact: contractor setup now takes under 10 minutes. The same document flow is the base for adding identity checks in payroll software.
AI risk models under compliance controls in a bank
Banks want machine learning in their risk processes, but only with controls their regulators accept. For a multinational retail bank, we built an AI platform for banking with custom predictive models, data pipelines that prepare millions of records daily, and a compliance and security layer with GDPR-ready monitoring, encryption, access controls, and logging of every action.
Impact: 35% less analyst workload and 40% faster decision-making, on a platform built for GDPR and PSD2 compliance.
Alert triage and SAR drafting with AI agents
AI agents read each alert, pull the transaction history and customer file, attach the evidence, and draft the SAR narrative. A compliance officer reviews and decides.
Impact: analysts spend their time on judgment calls. Research shows machine learning triage can cut false positives by 80% while keeping over 90% of true positives.
Travel Rule and stablecoin monitoring for crypto platforms
Crypto rules keep tightening. FATF reports that 83% of surveyed jurisdictions have passed Travel Rule legislation, and that most identified on-chain illicit activity now involves stablecoins. Your AML stack needs to send and receive originator and beneficiary data with every transfer and monitor stablecoin flows on-chain.
Impact: you meet Travel Rule requirements in each market you enter and lower your exposure to the type of penalties that made up almost a quarter of 2025’s top ten fines.
How Relevant builds AML and KYC software: a roadmap from risk map to launch
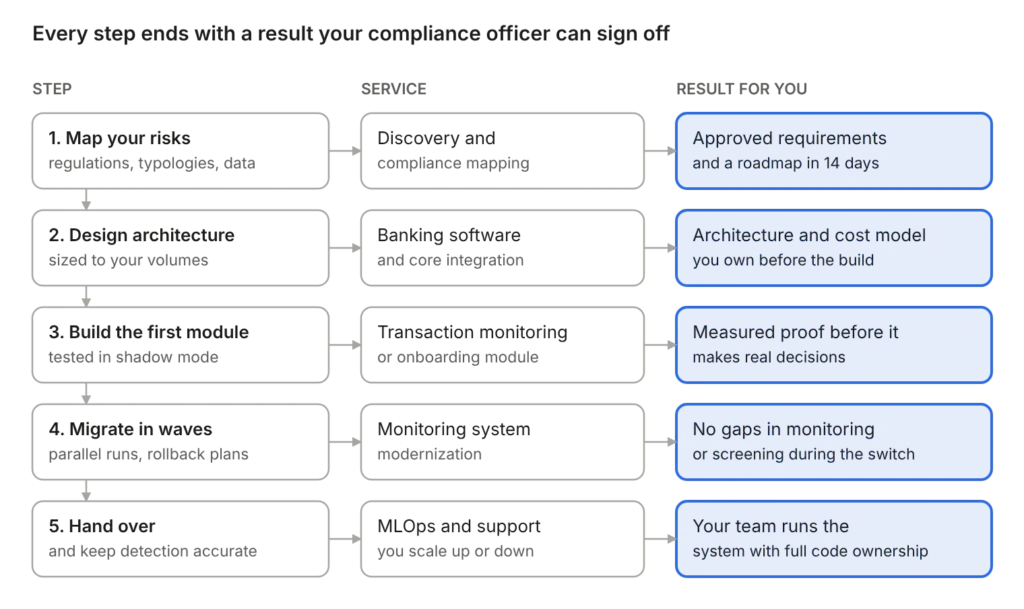
Compliance software has a constraint most products don’t: you can’t switch it off while you rebuild it. Our roadmap is designed around that. Each step ends with something your compliance officer can review and sign off.
Step 1. Map your risks, regulations, and data
We start with your transaction flows, customer types, jurisdictions, and the typologies in your own risk assessment. We map them to the rules that apply to you, such as the Bank Secrecy Act, the EU AMLR, FATF Recommendation 16, the Travel Rule, GDPR, PSD2, and DORA. We also audit your current core, data sources, and vendor contracts.
Result: a requirements document your compliance officer approves and a delivery roadmap within 14 days.
Step 2. Design an architecture sized to your volumes
Data pipelines, storage, and processing are sized to your real throughput and peak load. AML banking system integration is planned up front, covering your core banking system, KYC and AML data providers, card processors, open banking APIs, and regulatory reporting tools. The AML and KYC layer only works if it fits the core banking, lending, and payments software around it, so every integration point is mapped before anything else. Architecture, data flows, and controls are agreed with your compliance team before anyone writes code.
Result: an architecture and cost model you own before the build budget is spent.
Step 3. Build the first module and prove it on your data
We ship the module that carries your biggest risk first, often onboarding or transaction monitoring. Rules and machine learning models are built on your transaction history, backtested, and run in shadow mode on live traffic before they make a single real decision. The rule is the same one finance teams expect from AI-driven financial forecasting software: nothing ships until it beats what you run today.
Result: measured proof of fewer false positives or faster onboarding before you switch over.
Step 4. Migrate in waves without monitoring gaps
If you’re moving off a vendor platform, old and new systems run in parallel. We reconcile results, keep a rollback plan for each wave, and shift traffic step by step. Your coverage never drops, which matters when a regulator asks what happened during the switch.
Result: a new system in production with no blind spots in monitoring or screening.
Step 5. Hand over and keep detection accurate
Your analysts learn to configure rules, tune thresholds, run backtests, and use the reporting workflows. After launch, MLOps keeps models accurate with retraining pipelines, drift monitoring, and scenario updates. You get full code ownership and documentation, and you can scale our support up or down.
Result: a team that runs the system independently, and detection that stays sharp as criminals adapt.
How long AML and KYC software development takes and what changes the timeline
We don’t quote a timeline before discovery, because scope varies too much from one compliance stack to the next. What we can share is how the phases run and what moves the dates.
- Discovery and roadmap: 14 days.
- First release: our fintech MVPs have gone live in 3 months for FirstHomeCoach and in 4 months for Poncho. The first AML or KYC release is planned the same way: one focused module, live, then the next.
- Expansion and migration: added in waves, each with its own parallel run and sign-off.
AI-assisted delivery shortens build phases by up to 50% with up to 20% fewer errors, and every line of code still passes senior review.
What changes the timeline most:
- Scope of modules. KYC software development for onboarding alone is a smaller project than AML software development with monitoring, case management, and SAR filing.
- Number of jurisdictions. Each market adds its own rules, lists, and reporting formats.
- Integrations. Every core banking system, IDV vendor, and data provider needs its own connector, and older systems usually need more work.
- Migration from a legacy vendor. Parallel runs and reconciliation add time and remove risk.
- Rules or machine learning. ML models need clean historical data, backtesting, and documentation that satisfies model risk management.
- Audit and data retention requirements. Detailed audit trails and long retention periods shape the data architecture from day one.
- Your team’s availability. Compliance sign-offs at each step keep the project safe, and they move faster when a decision-maker is assigned early.
AML and KYC software development case studies: results in numbers
These three projects cover the main paths: a hybrid fintech launch, a full replacement of a vendor platform, and AI built under strict compliance controls.
Fisk: KYC and financial APIs orchestrated into one fintech product
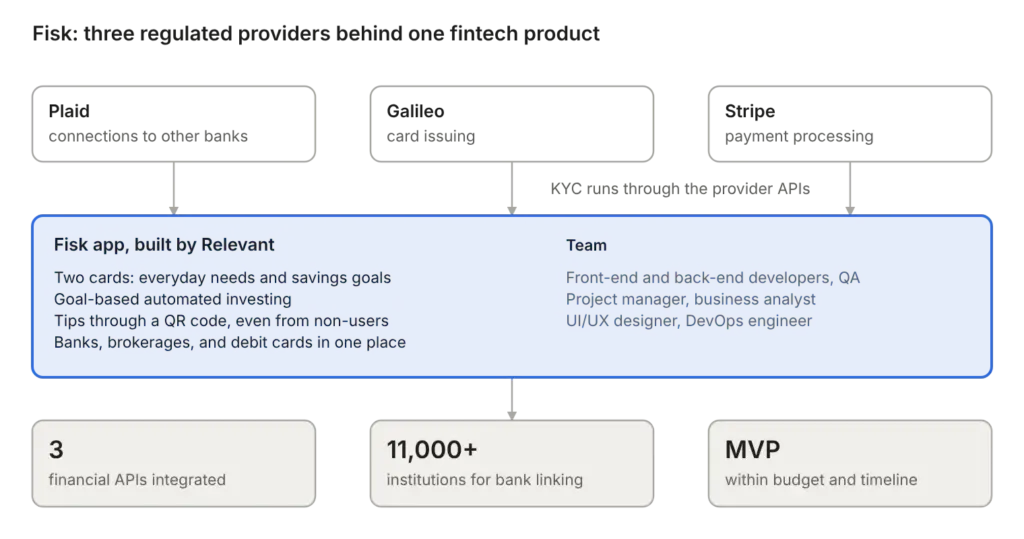
Challenge. Fisk, the first digital product of US-based 55th Degree, needed an MVP for automated investing and virtual card tipping. The product depended on several regulated services at once: KYC, card issuing, payment processing, and connections to users’ accounts at other banks. Each came from a different provider with its own API and rules.
Solution. Our team, with front-end and back-end developers, QA, a project manager, a business analyst, a UI/UX designer, and a DevOps engineer, built the product around Plaid, Galileo, and Stripe. Users get one card for everyday needs and one for savings goals, invest toward a goal, receive tips through a QR code (even from people without the app), and link multiple banks, brokerage accounts, and debit cards in one place.
Results.
- 3 financial APIs integrated, covering KYC, cards, and payments
- 11,000+ institutions available for bank linking through Plaid
- MVP delivered within the agreed budget and timeline, with the client’s sales process started and users asking for phase two
“Having an outsourcing team has enabled us to concentrate more on innovation and company structure.” Jessica Dawson, CEO of 55th Degree
Caribbean lender: a custom platform in place of an expensive vendor
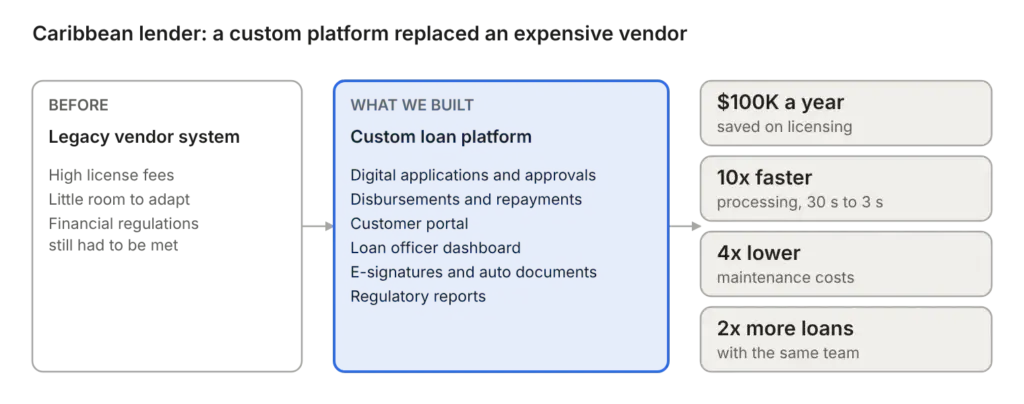
Challenge. A licensed loan company in the Caribbean ran on a legacy system with high license fees and little flexibility. It needed a platform that met financial regulations and grew with the business.
Solution. We built a loan management platform from scratch. It covers digital applications, approvals, disbursements, and repayments, with a customer portal, a loan officer dashboard, automated documents and e-signatures, and regulatory reports such as Long Aging, Principal Changes, and Deferred Fees.
Results.
- $100,000 saved every year on software licensing
- 10x faster processing, from 30 seconds to 3 seconds per loan
- 4x lower maintenance costs
- 2x more loans processed with the same team
“We are pleased to recommend Relevant Software as a strategic technology partner.” CEO & CFO, Caribbean loan company
Multinational bank: AI risk models with a built-in compliance layer
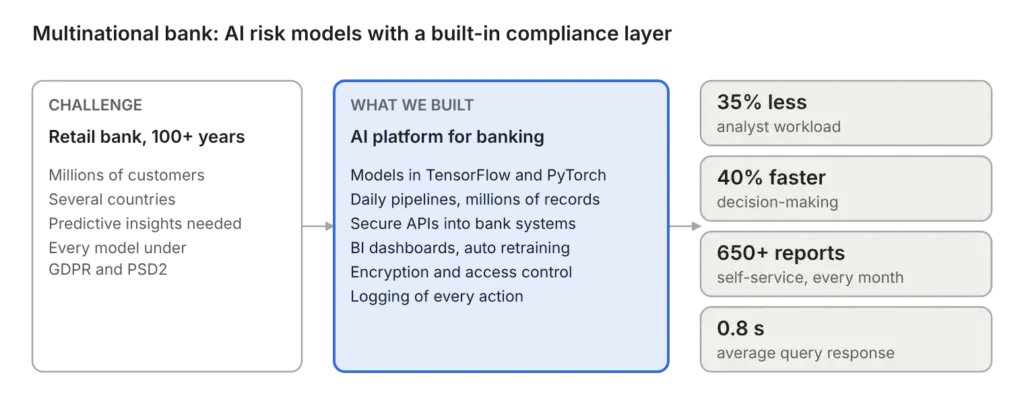
Challenge. A bank with over a century of history, serving millions of individuals and small businesses in several countries, wanted predictive insights for savings, cards, loans, and insurance. Every model had to run under GDPR and PSD2.
Solution. Together with CX Design, we built an AI platform for banking: custom predictive models in TensorFlow and PyTorch, data pipelines that clean and prepare millions of records daily, secure APIs into the bank’s systems, BI dashboards, and automated retraining. A compliance and security layer adds GDPR-ready monitoring, encryption, access controls, and logging of every action.
Results.
- 35% less analyst workload
- 40% faster decision-making
- 650+ self-service reports generated monthly
- 0.8 s average query response time
“They had the talent to keep positive momentum with both to-the-point communication and humor when necessary.” Founder & CEO
The same compliance layer, audit logging, and retraining pipelines are what AML models need to pass a model risk review.
Why banks and fintechs choose Relevant for AML and KYC software development
We’ve built custom software since 2013, and more than 10 of those 13 years have been in fintech and regulated industries. Here’s what that looks like in numbers:
- 246 projects delivered
- 99% of projects delivered on time and on budget
- 14 days to a delivery roadmap
- 92% senior engineers and 96% employee retention
- 98% client satisfaction and a 4.9 average rating on Clutch
- ISO 27001:2022 certified processes and GDPR coverage
Whether you need KYC software development for one onboarding flow or a full AML stack, tell us what you run today, and our experts will get back to you within 24 hours with next steps. We sign an NDA if you need one, then send a detailed proposal with estimates, timelines, and team CVs.


